
Check Point recorded 31 public ransomware claims and 24,875 data exposure incidents in the Philippines between January and August 2026.
Check Point Software Technologies has reported a rise in ransomware, data exposure, and social media impersonation threats targeting organisations in the Philippines during the first eight months of 2026.
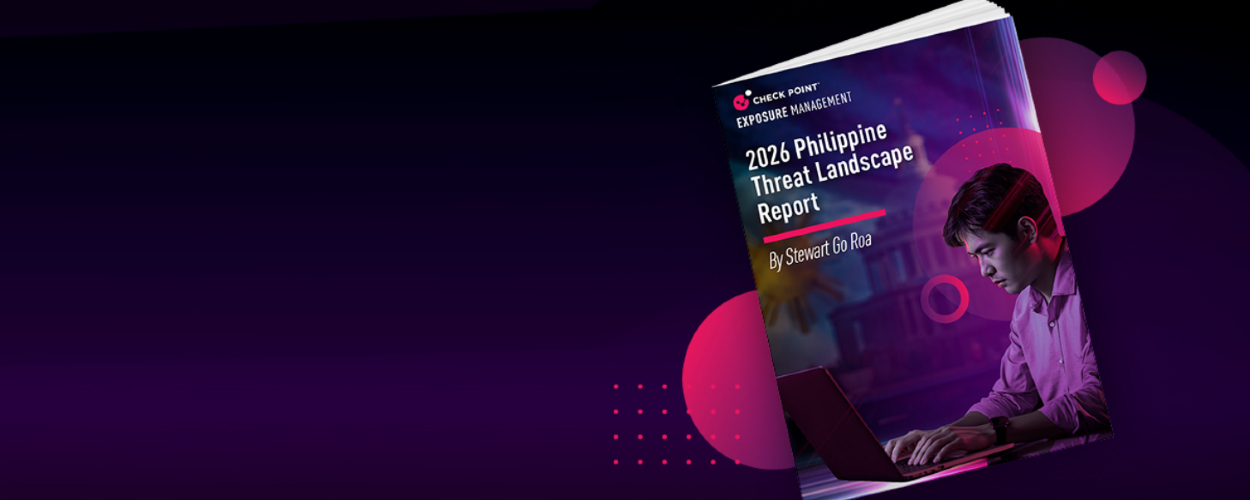
The company’s 2026 Philippines Threat Landscape Report recorded 31 public ransomware claims against Filipino organisations through August, surpassing the 26 claims recorded across 2024 and 2025 combined. Fifteen ransomware groups made local claims during the period, compared with 12 across all of 2025.
Qilin remained the most active group in the local dataset, accounting for 29% of claims in 2026, up from 23% in 2025, according to Check Point.
The report also tracked 24,875 data exposure incidents. Nearly 44% involved malware extracting credentials from infected devices, while almost 24% involved exposed payment card data and 10% involved employee credentials leaked through third-party platforms.
Phishing activity remained relatively stable at 2,386 alerts, but Check Point said attackers shifted towards fake reward points and loyalty programme updates designed to obtain personal and payment information.
Social media impersonation also increased, with 1,194 alerts recorded. Facebook was involved in around four-fifths of the cases, while TikTok was frequently used for executive impersonation.
Cybercriminals were increasingly using artificial intelligence for social engineering rather than directly compromising technical systems. The company cited deepfake videos, cloned voices, and AI applications as tools used in scams, fraud, and malware distribution.
Recommendations to remedy these issues include strengthening identity security, monitoring internet-facing systems, and establishing stronger controls over enterprise AI.
Stay updated on crypto and AI by following our socials.